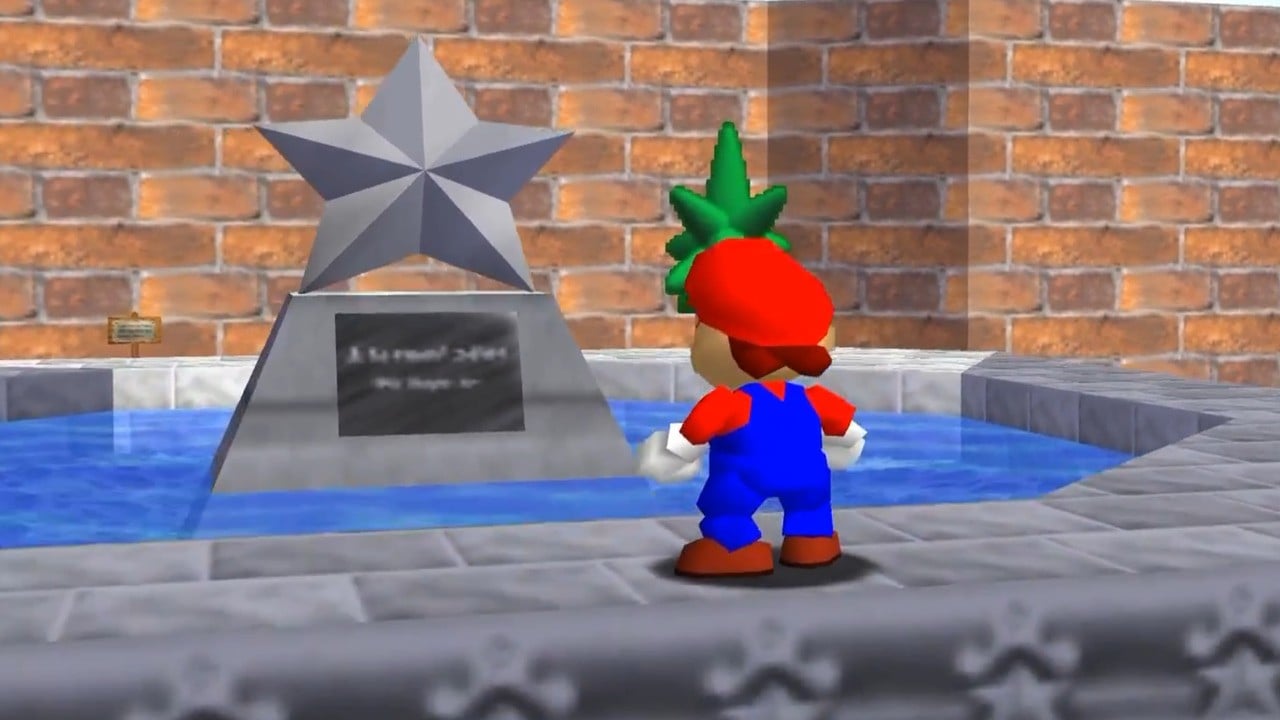

A reported jailbreak of the Nintendo Switch 2 was demonstrated publicly on October 22, 2026, when Twitter user @pepsipu posted a clip showing a modded version of Mario Kart World and claimed to have gained low-level software access to the new console.
The demonstration — which swapped in characters such as Cinnamoroll, Peter Griffin and Hatsune Miku — prompted immediate attention from developers and security observers focused on Nintendo platform integrity.
According to the public post and an accompanying blog thread, the exploit used by pepsipu required a multi-device setup and specific software components.
The process as described involves: access to both a Nintendo Switch (original) and a Nintendo Switch 2, a PC on the same local network running Node.js 22 or newer, and the SmileBASIC Switch application at version 4.4.9, including roughly 20 MB of save data extracted from the SmileBASIC title.
The jailbreak is not persistent; the user must repeat the sequence each time the console is restarted.
In his post, pepsipu wrote that he had "jailbroke the Nintendo Switch 2" and modded several character models into Mario Kart World, and later acknowledged using OpenAI tools to assist in discovering the exploit vector.
Rewritten for clarity: the user reported successfully using an OpenAI-assisted research workflow to identify a software-level vulnerability that allowed code modification within Mario Kart World on Switch 2 hardware.
This report contains several verifiable technical details: the tweet timestamp (October 22, 2026), the specified SmileBASIC version (4.4.9), the Node.js minimum version (22+), and the approximate save-data size involved (20 MB).
These particulars were presented by the demonstrator and are relevant to developers and security researchers assessing the scope of the issue.
At present the exploit appears to be a software-level, non-persistent bypass requiring developer tools and multiple devices, which limits immediate risk of widespread piracy.
The demonstration does not constitute an official Nintendo statement; no public response from Nintendo was included with the initial disclosure.
Given the nature of software vulnerabilities on console platforms, platform holders typically issue updates to address disclosed exploits.
For the industry, this incident highlights both the continuing cat-and-mouse dynamic between console security and independent researchers and the real-world role of large-language-model tools in accelerating vulnerability discovery.
Readers should avoid attempting unverified exploits on their hardware and monitor official channels such as Nintendo's eShop and patch notes for any future updates or advisories.